CosmicSting (CVE-2024-34102) is an XML external entity flaw in Magento 2 and Adobe Commerce, fixed in Adobe’s APSB24-40 and published on NVD on 13th June 2024. Unpatched, it lets anyone read files the PHP user can read, including app/etc/env.php and the encryption key in it. Combined with the glibc iconv bug, it turned into remote code execution.
Two groups needed an answer quickly. Merchants needed to know whether their store was still exposed, without reading an exploit. And we needed to check every store we host, including the ones nobody remembered. I built a hosted checker for the first and published the bulk tooling for the second.
The online validator runs my PHP port of Chocapikk’s public PoC. The CLI tools wrap the original Python, lightly modified, as poc.py.
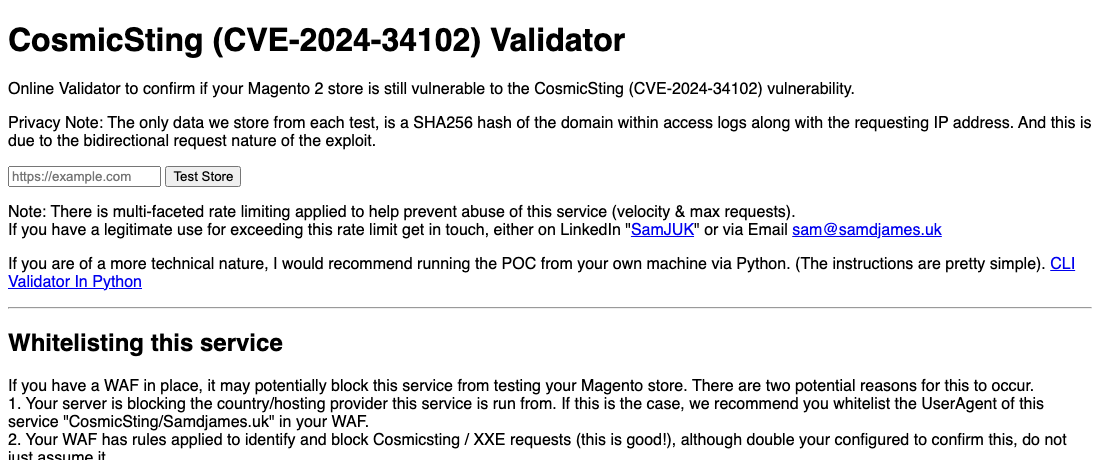
Is my Magento store still vulnerable to CosmicSting?
Paste the store URL into the online validator and it returns one of three results: vulnerable, safe, or a 403. A 403 may still be safe; it usually means a web application firewall stepped in. If you get one and want certainty, run the CLI below from your own machine.
It is aimed at merchants rather than agencies, and built to be careful with what it touches:
- The only data kept per test is a SHA256 hash of the domain in the access logs, alongside the requesting IP. The exploit is a two-way request, so the server has to see the callback.
- Rate limiting caps both velocity and total requests.
- Requests identify themselves with the user agent
CosmicSting/Samdjames.uk, so WAF owners can allow them.
How do I check a list of stores?
Put the URLs in a text file, one per line, and run the wrappers in the repo against it:
./poc.py -u https://example.com        # one store
./z_validate sites/hosted.txt          # every store in a list
./z_compromise_check sites/hosted.txt  # diff each site's external scripts against the last run
check.bash loops a SITES array and exits with status 255 if any site comes back vulnerable, so it can gate a scheduled job. z_compromise_check snapshots each site’s off-domain <script src> list and diffs it against the previous run, a basic way to spot a newly injected skimmer.
Is patching enough?
No. The fix itself is a single-file change to ServiceInputProcessor.php, but anything the PHP user could read before it went on may already have been taken. Rotate the encryption key in app/etc/env.php as well. The maintained reference is the CosmicSting docs page.
What did it find?
Stores nobody remembered. Piping our exported DNS records through the bulk check found publicly available demo stores and development sites that had been missed. I held the write-up back to give stores time to patch first.
History
- 13th June 2024: CVE-2024-34102 published on NVD.
- 25th June 2024: first commit, the proof of concept wrapper and
check.bash. - 7th July 2024: the write-up published.
- 12th July 2024: online validator linked from the README.
- 13th July 2024:
z_validateandz_compromise_checkadded for lists of stores.